AI · 2 Nov 2026 · 18:41 CET
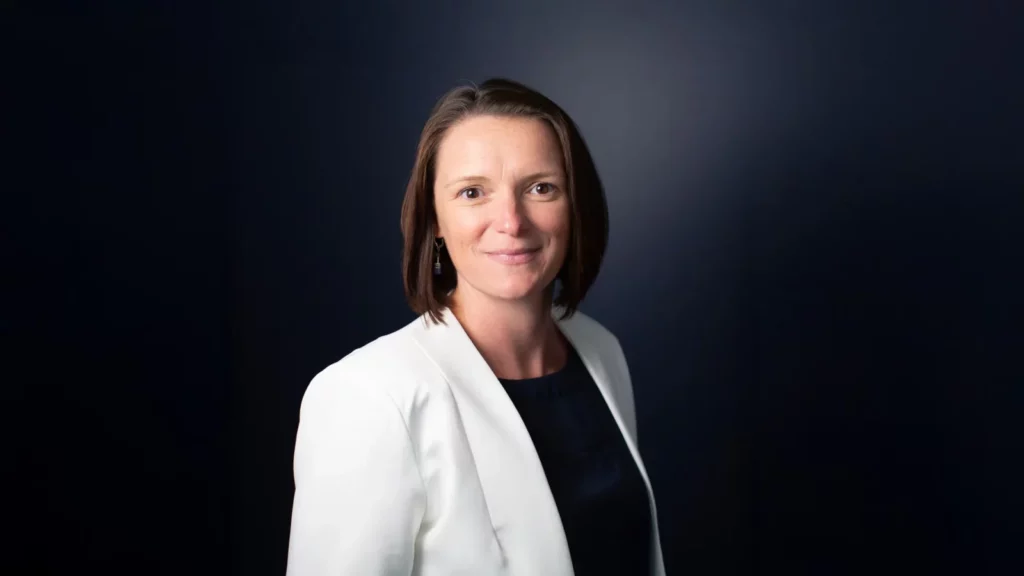
Sarah Webb, COO and Co-Founder of LawVu – Interview Series
Publisher preview · OZZZER analysis pending editorial review.
PUBLISHER ARTICLE PREVIEW
From the original article
Sarah Webb is COO and Co-Founder of LawVu, bringing a background in engineering and software leadership that includes roles at LOVEFiLM and Amazon. She joined LawVu as CTO in 2015 and became COO in 2020, combining experience across technology, operations, security, and governance. Her work focuses on helping legal teams connect their data and workflows while balancing AI innovation with enterprise risk.
LawVu provides a legal operating system for in-house legal teams, bringing intake, matters, contracts, spend, and knowledge into a connected platform. Its AI capabilities and integrations help teams work across their existing tools while maintaining permissions and oversight. In this interview, Webb discusses shadow AI, agentic workflows, institutional knowledge, and the foundations enterprises need for governed AI adoption.
You co-founded LawVu after spending much of your career building and leading software teams, including at LOVEFiLM and Amazon. What led you to identify corporate legal operations as a problem worth solving, and how has your original vision for LawVu evolved as AI has transformed the technology landscape?
I spent most of my early career in engineering and technology roles, including LOVEFiLM and Amazon, and the move into legal tech wasn’t something I set out to do, it happened more by circumstance. I’ve been at LawVu for almost 11 years now, originally as CTO, but with a fairly quick move to COO, and that shift alone has changed a lot about how I think about the business.
In the early days, the first problem we were solving for was visibility. Most customers were coming off Outlook and Excel spreadsheets, and just getting everything into one place felt like a real win. Then we moved into a period where teams went remote, and without a centralized platform, collaboration got even harder. That reinforced something we were already seeing, which is that a lot of repetitive legal work wasn’t being valued or even seen by the rest of the business, because there was nowhere for it to be visible.
That period pushed us to do real education work with customers on how to structure their data and manage the change internally, not just hand them a tool.
We also built out integrations across the Microsoft suite early on, because the goal was always to meet the business where it already worked day to day, rather than asking teams to abandon what they knew. What’s changed since then is the scale of what that same idea now demands. Reducing the barrier to entry to get a usable dataset used to be about convenience.
Now it’s the difference between AI that can actually act on legal work and AI that’s just reflecting the same fragmentation back at you.
You’ve argued that “shadow AI” is often a workflow problem rather than an employee problem. What does that mean in practice, and what can organizations learn when employees bypass approved AI tools or systems in favor of their own solutions?
If you don’t make the right tooling available internally, people will go find their own for the efficiency gains. That’s the root of it. When someone bypasses an approved system, the instinct is to treat it as a compliance failure, something to lock down or write a policy against. In practice, it’s usually telling you something about the workflow itself, that the approved path was slower or more painful than the alternative, so people found their own way around it.
That’s exactly why shadow AI is a bigger liability than shadow IT ever was. Incidents involving shadow AI now account for 20 percent of data breaches, at an average cost of 10.2 million dollars, because people aren’t just adopting an unapproved tool, they’re feeding it the sensitive material directly, contract language, deal terms, internal reasoning.
What organizations should actually learn from this is where the gap is. The absence of a secure, grounded alternative doesn’t stop people from turning to AI, it just pushes them toward doing it somewhere you can’t see. And there’s a deeper risk underneath that, one that goes beyond security. When work is scattered across personal AI tools instead of a shared, structured system, the business ends up making decisions on an incomplete picture, without even realizing part of the picture is missing.
If an AI tool can only see 60 percent of the relevant data because the rest is sitting in someone’s own account, its accuracy drops and the risk of a wrong call goes up. Banning the workaround doesn’t fix any of that. Giving people something better than the workaround does.
Through LawVu’s work with hundreds of enterprise legal teams, what are the most common mistakes you see organizations making when establishing AI governance, particularly as employees gain access to increasingly powerful general-purpose AI tools?
The most common one is mistaking a written policy for an actual control. Plenty of organizations have a document now that says how AI should and shouldn’t be used. Very few have built anything operational behind it, something that actually governs what a tool can access, logs what it did, and lets you reconstruct that afterward if you ever need to.
The second mistake is not accounting for how much risk gets added one tool at a time.
Source
Unite.AI · 2 Nov 2026 · 18:41 CET
Open the original at Unite.AI ↗